How to Secure AI Agents, MCP Servers, and LLM Apps in Production
MarkTechPost 2 months ago 47
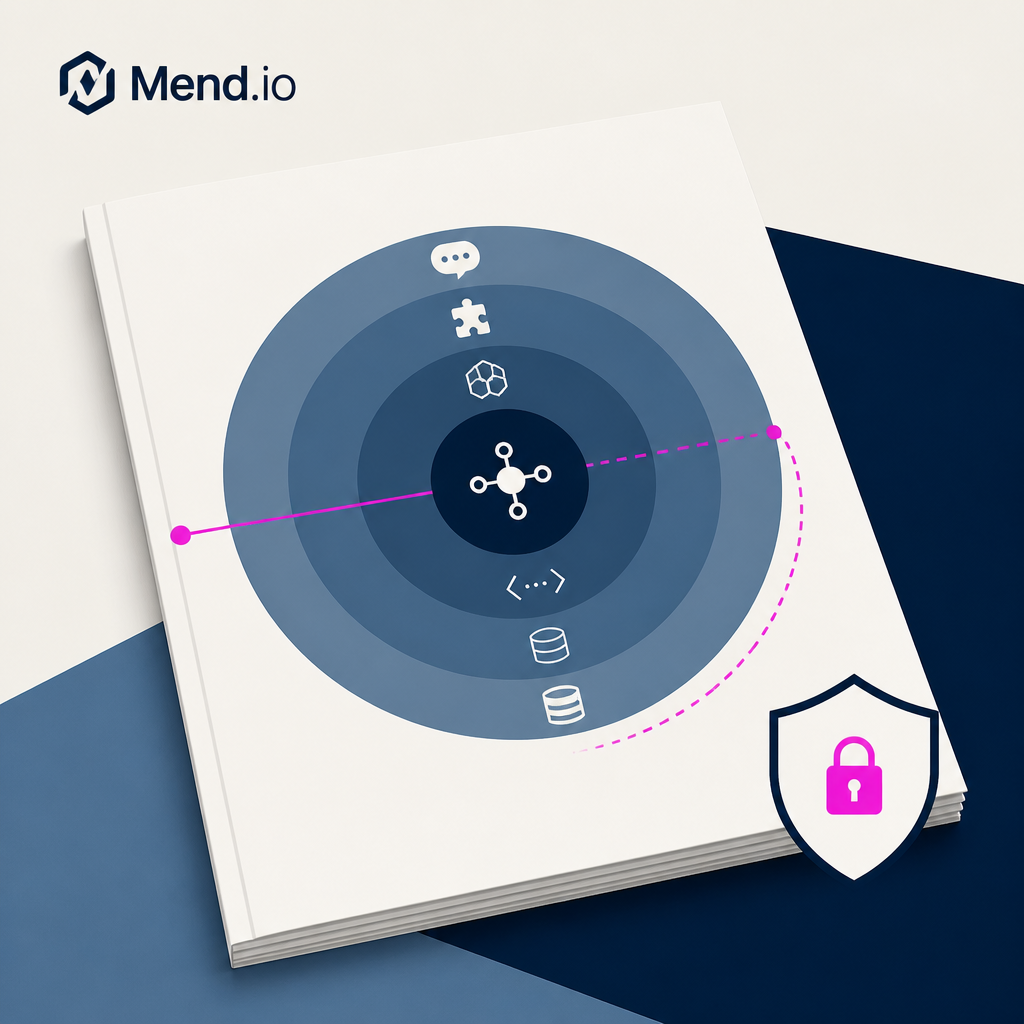
Mend.io published a security framework for AI agents, MCP servers, and LLM applications that addresses how traditional application security fails when agent behavior emerges unpredictably from models, prompts, and tool integrations. The guide provides a five-layer attack surface map covering interactions, agents, integrations, models, and code, plus discovery methods for shadow agents and unregistered servers. Organizations should automate evidence-backed triage while applying runtime guardrails, system prompt hardening, and strict permission controls to protect agentic systems in production.