The Topology of an LLM Agent Loop With Tool Use
exe.dev
New LLM agents are being judged by where the model, loop, and tools run. That setup changes cost, privacy, security, and who pays when the agent goes off-script.
Based on reporting by exe.dev — read the original for the full story.
Summary, retelling and take written by AI under human oversight; images are AI-generated illustrations. How we work · Report an error
When someone looks at a new agent, the first useful question is not “How smart is it?” It’s where everything lives. The model, the loop, and the tools each sit somewhere, and that topology shapes what the product can do, how much it costs, and how risky it is.
Start with the model. If it runs on someone else’s GPUs, you’re trusting that setup with your data. If it runs locally, privacy is easier to reason about, and speed may matter less when the job can run overnight. That’s why local models make sense for tasks like OCR and classifying scanned bills on a machine you control.
Then there’s the loop itself. In ChatGPT, the loop runs on OpenAI’s servers. In a coding agent, it may run on a laptop. It can also run in a browser. The loop keeps the full message history, stores it somewhere, and decides the interface: images, video feedback, attachments, sharing, or just plain text. Different loops feel restrictive for different reasons, and people often prefer their own over someone else’s.
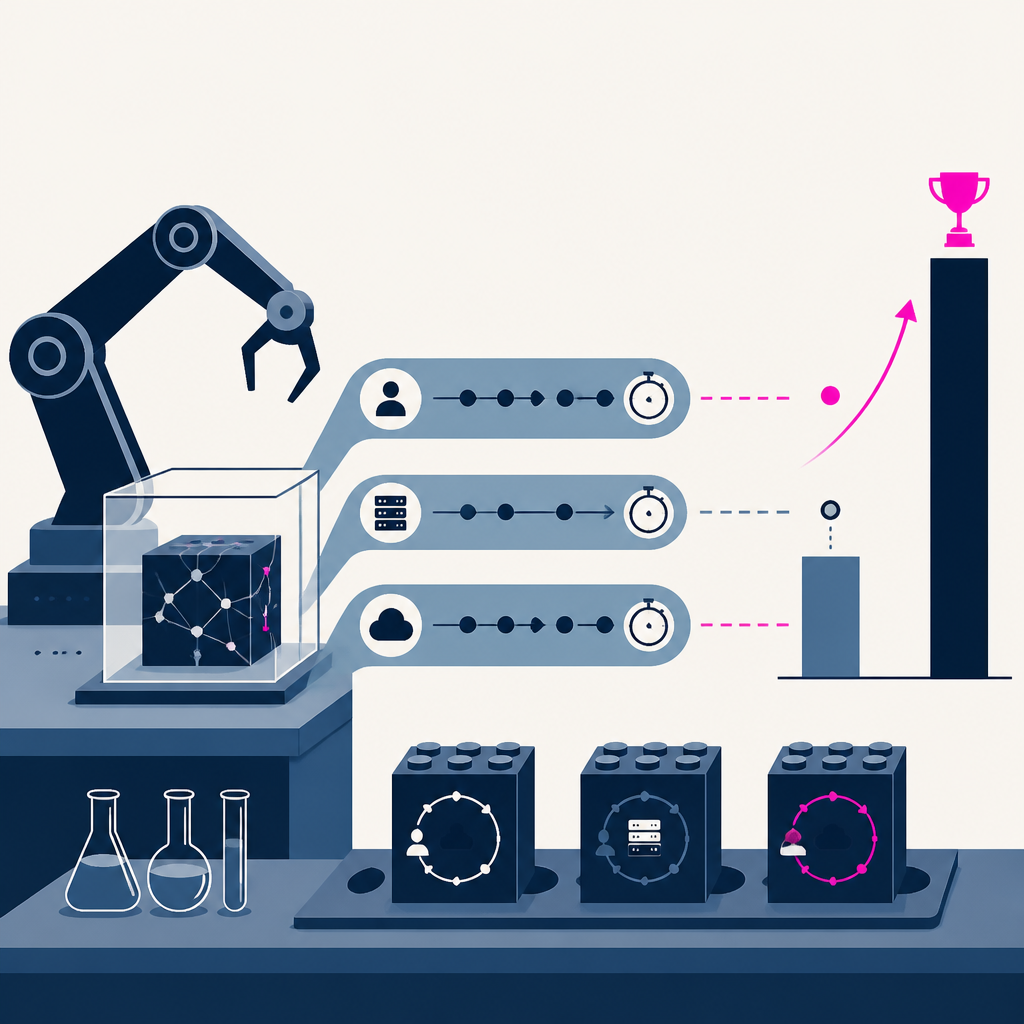
Tools are where the blast radius shows up. Once an agent can execute code, it can do real work: edit files, compile, process video, run tests. That’s also where the danger sits, which is why virtual machines are treated as the gold standard. Even then, the details matter: network access, credentials, memory, and whether the code is trusted. Readonly SQL or sandboxed WASM can narrow the risk, but the questions never go away.
This is also a business problem now. A diagram SaaS that lets an agent edit diagrams is no longer just paying for database rows. A customer can burn through tokens fast. That’s why bring-your-own-model setups are starting to look less like a niche idea and more like a practical one. And it’s why products that make themselves legible to agents may win more often than polished products that stay closed off.
My take — AI-written commentary, not fact-checked reporting
The industry keeps pretending an agent is a product feature, when it’s really a wiring diagram with opinions. The companies that will do well are the ones that make the wiring obvious and the blast radius small, not the ones that wrap everything in a cheerful chatbot and call it strategy. Agent hype is cheap; clean topology is the actual work.
Read more about this at: exe.dev